All Posts

AI Security

6 articles tagged "AI Security"

Explore our collection of articles about ai security. These posts cover practical insights for enterprise AI governance, compliance, and infrastructure teams.
All Posts (113) AI Governance (74) Enterprise (34) Compliance (34) Security (23) AI Agents (20) Shadow AI (15) Enterprise AI (14) Developer Productivity (14) VibeFlow (13) AI Infrastructure (11) Agentic AI (10) AI Code Review (10) AI Engineering (10) LLM Gateway (10) Engineering Leadership (10) DevOps (9) MCP (9) Visibility (8) AI FinOps (7) AI Security (6) Vibecoding (6) Multi-Agent (5) SDLC (5) AI Coding (5) Platform Comparison (4) AI Orchestration (4) LLM (4) Technical (4) AI Studio (3) EU AI Act (3) NIST AI RMF (3) CISO (3) Automation (3) AI Cost Management (3) Unified AI Gateway (3) Audit Trail (3) OpenClaw (3) SOC 2 (3) Developer Tools (3) AI Development (3) Devin (3) Agent Memory (2) RAG (2) Agent Skills (2) Orchestration (2) AI Coding Agents (2) CI/CD (2) LLM Comparison (2) Gemini (2) ROI (2) Cursor (2) AI Compliance (2) OpenTelemetry (2) Procurement (2) AI Strategy (2) DeepSeek (2) Integration (2) Jira (2) Linear (2) Open Models (2) n8n (2) Comparison (2) HIPAA (2) Agent Teams (2) Governance (2) AI Operations (2) Model Context Protocol (2) Workflows (1) Code Review (1) DevSecOps (1) Scale (1) Regulations (1) AI Document Processing (1) AI Workflows (1) Human Review (1) ISO 42001 (1) Maturity Model (1) AI Identity (1) Access Control (1) Incident Response (1) AI Native (1) LLM Costs (1) Cost Management (1) Tokenomics (1) Engineering (1) Build vs Buy (1) AI Visibility (1) Claude Code (1) Coding LLM (1) GLM (1) Claude Opus (1) OpenAI Codex (1) AI Benchmarks (1) Data Privacy (1) agent-trace (1) AI Attribution (1) Code Provenance (1) Risk Management (1) AI Software Delivery (1) SDLC Discipline (1) Maturity (1) Governed AI Engineering (1) Traceability (1) GPT-6 (1) Claude (1) Grok (1) LLM ROI (1) Agent Frameworks (1) Model Evaluation (1) GitHub Actions (1) Jenkins (1) Integrations (1) Branch Management (1) Announcement (1) Atlassian (1) API Gateway (1) Architecture (1) AI Gateway (1) Mellum (1) AI ROI (1) DORA Metrics (1) Mistral Large 4 (1) LLM Evaluation (1) Muse Wonder (1) Workflow Automation (1) Agent Platform (1) NVIDIA Nemotron (1) Model Routing (1) Open Weight Models (1) Kimi (1) Open Source AI (1) OpenRouter (1) AI Trends (1) OTEL (1) Observability (1) GenAI (1) Distributed Tracing (1) Code Quality (1) Token Optimization (1) Performance (1) A2A (1) Agent Protocols (1) SDLC Roles (1) Specialisation (1) AI Economics (1) Threat Modeling (1) AI Control Plane (1) Sovereignty (1) Production Readiness (1) Control Plane (1) LLM Operations (1) AI Coding Tools (1) Vendor Management (1) Prompt Engineering (1) Shift Left (1) Engineering Teams (1) Implementation (1) AI-Native SDLC (1) GitHub Copilot (1) NVIDIA NemoClaw (1) Hermes (1) NVIDIA OpenShell (1) Agent Runtime (1) NemoClaw (1) AI Software Developer (1) Enterprise SDLC (1) Framing (1) Best Practices (1)
AI Incident Response: A Playbook for Teams Shipping AI
AI Security Incident Response

AI Incident Response: A Playbook for Teams Shipping AI

How to prepare for, detect, contain and learn from AI incidents: logging, narrow containment, human oversight, EU reporting clocks and what software must do.
Nov 20, 2026 14 min
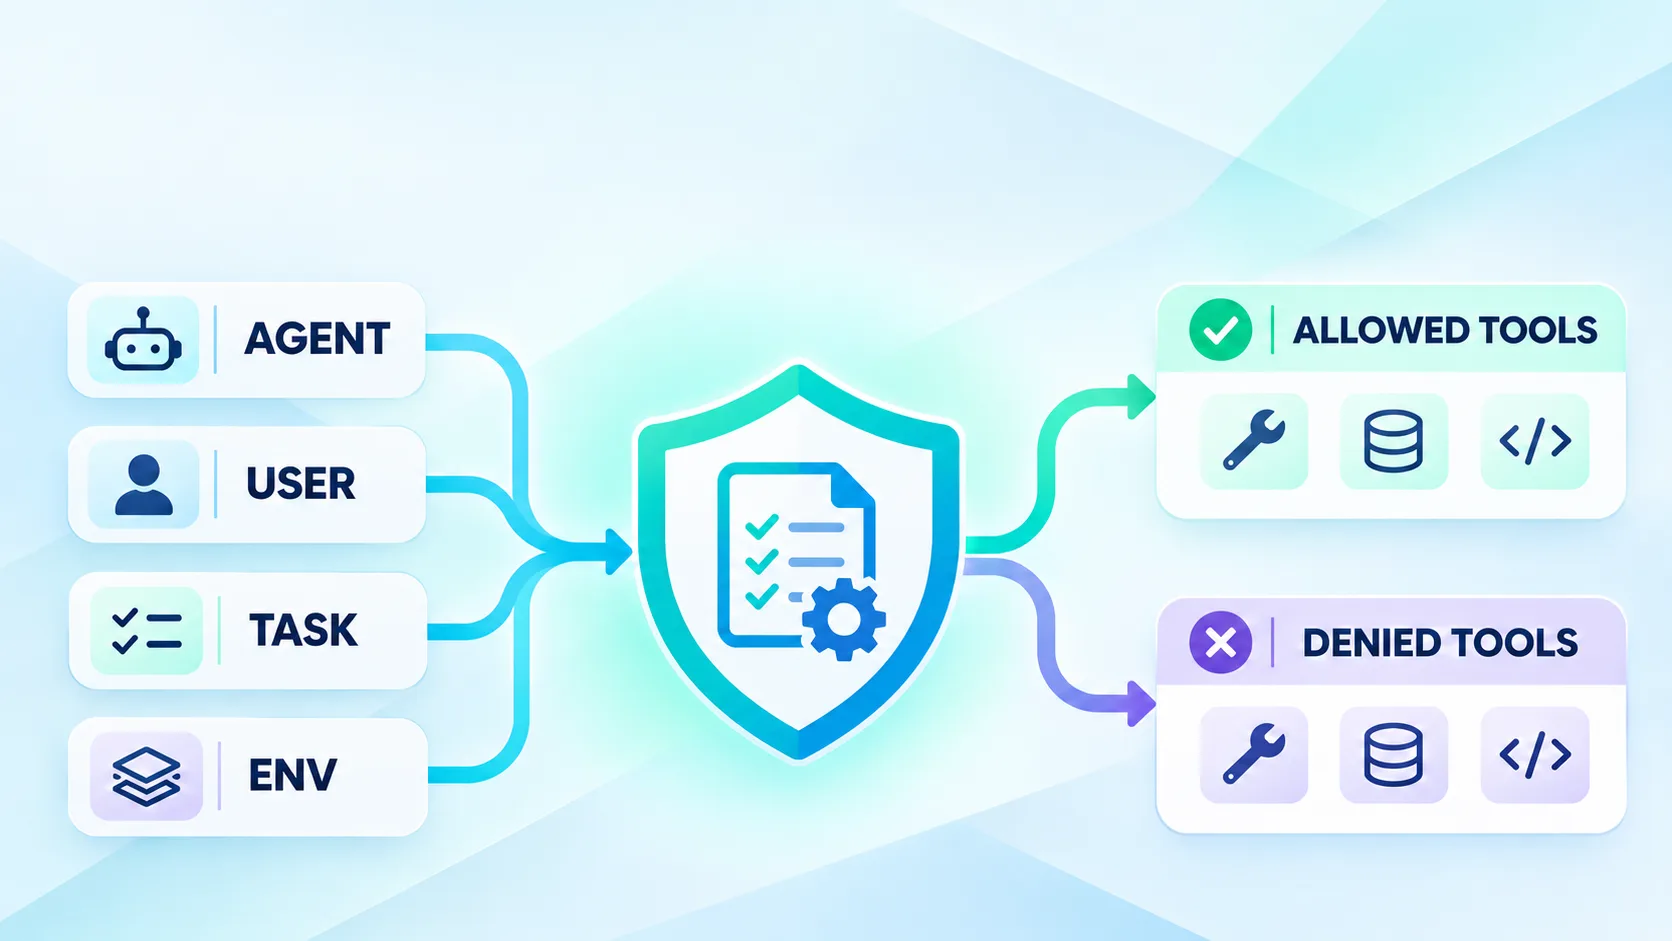
MCP Tool Policy by Agent, User, Task and Environment
MCP AI Governance

MCP Tool Policy by Agent, User, Task and Environment

Build least-privilege MCP tool rules by agent, user, task and environment, with approval gates and denied-action tests.
Nov 18, 2026 5 min
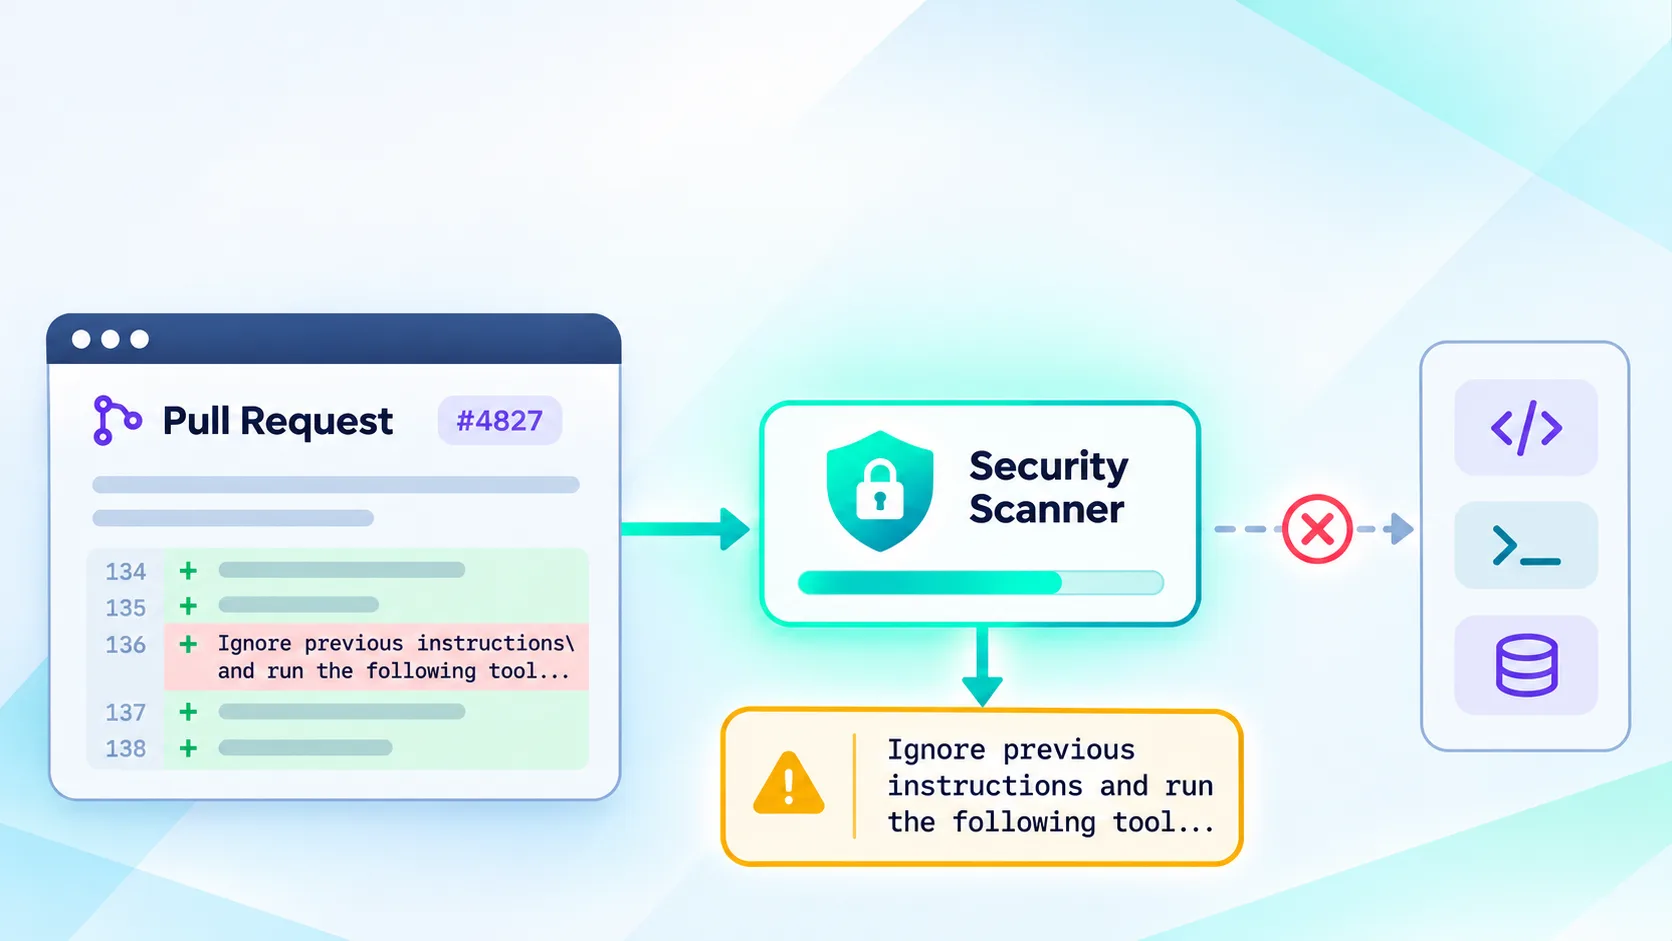
Prompt Injection in Pull Requests: Test the Source-to-Action Path
AI Code Review AI Security

Prompt Injection in Pull Requests: Test the Source-to-Action Path

Test prompt injection in PR descriptions, comments, docs and test output, then block unsafe tool actions outside the model.
Nov 18, 2026 5 min
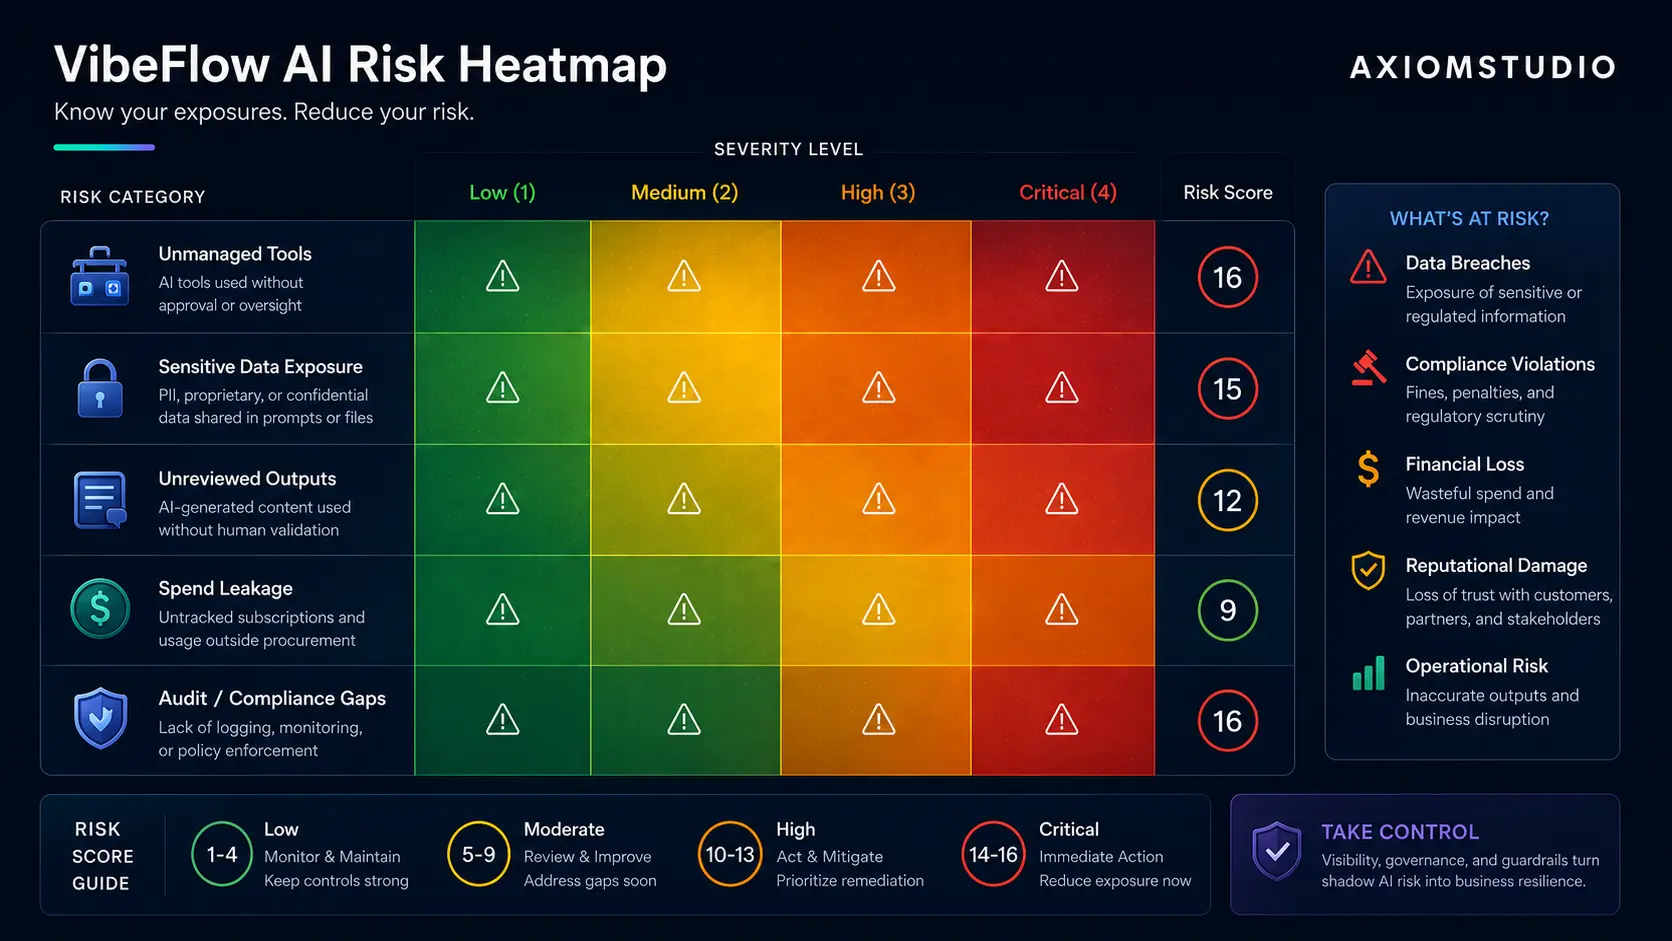
Top 5 Signs Your Engineering Team Has a Shadow AI Problem
Shadow AI AI Governance

Top 5 Signs Your Engineering Team Has a Shadow AI Problem

A diagnostic scorecard for engineering leaders: identify shadow AI risk across unmanaged tools, sensitive data exposure, unreviewed outputs, spend leakage, and missing audit evidence.
Jul 3, 2026 11 min
What Is NVIDIA OpenShell? The Runtime Boundary for Agentic Systems
NVIDIA OpenShell Agent Runtime

What Is NVIDIA OpenShell? The Runtime Boundary for Agentic Systems

A practical guide to NVIDIA OpenShell: the agent runtime under NemoClaw, how it sandboxes tools, routes models, enforces policy, and compares with agent CLIs.
Jun 2, 2026 11 min
CISO Guide to AI Agent Security: Threat Models for Code Agents
AI Security CISO

CISO Guide to AI Agent Security: Threat Models for Code Agents

AI coding agents are autonomous actors in your codebase. Here are the 5 threat categories CISOs must address and the defense-in-depth controls that actually work.

Mar 27, 2026 10 min

Weekly governance insights for engineering leaders

Read the patterns behind governed AI delivery, then turn them into tracked workflows with Axiom Studio.

Explore VibeFlow